Each platform owns a discipline and shares a single architecture, so output is consistent, traceable and defensible wherever it originates.

Consolidating audit, risk, policy and third parties
Running site audits and issuing the report
Learn moreEstablishing one risk position across locations
Learn moreGoverning consent and data principal rights
Learn moreMonitoring criminal cases and fraud matters
Learn moreTracing assets and land records at scale
Learn moreStandardising fraud assessment across desks
Learn morePreserving institutional memory
Learn morePreserving institutional memory
Learn moreEvery product shares one architecture — evidence held in one is available to the next.
Regulatory obligation made measurable, auditable and continuous. The platforms are engaged separately and share one architecture, so evidence held in one is available to the next.
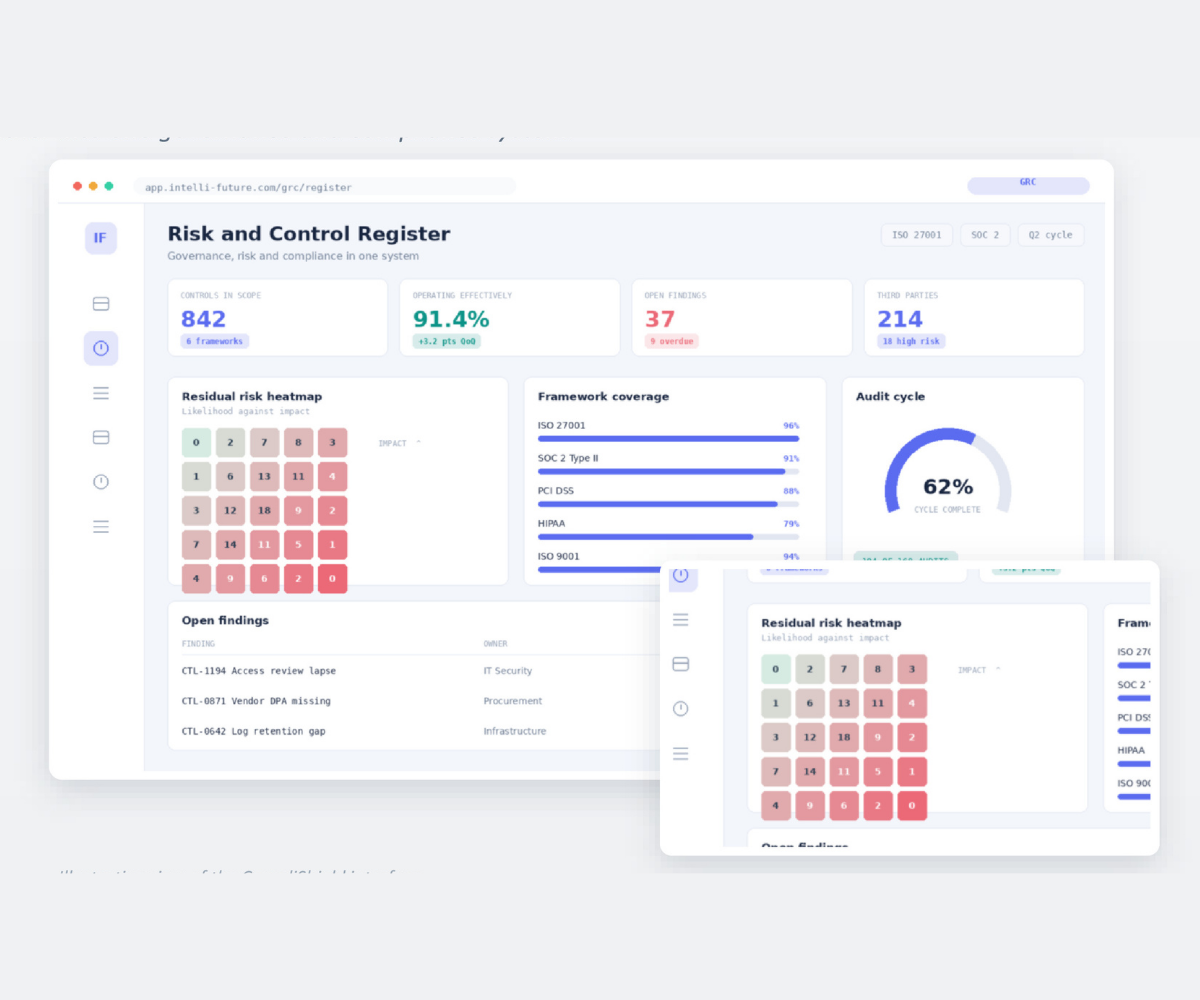
One governance register holding audit, risk, policy and third parties together, with the evidence attached to each.
CompliShield holds audit, risk, policy and third party oversight in a single register. The consolidated position is therefore continuous, and available on the day an inspection asks for it rather than assembled in response to one.
Financial services institutions under frequent regulatory change, healthcare providers holding patient data obligations alongside accreditation, manufacturing groups running multi site audit programmes, technology organisations maintaining several certifications on overlapping cycles, and energy and utilities operators under continuous scrutiny.
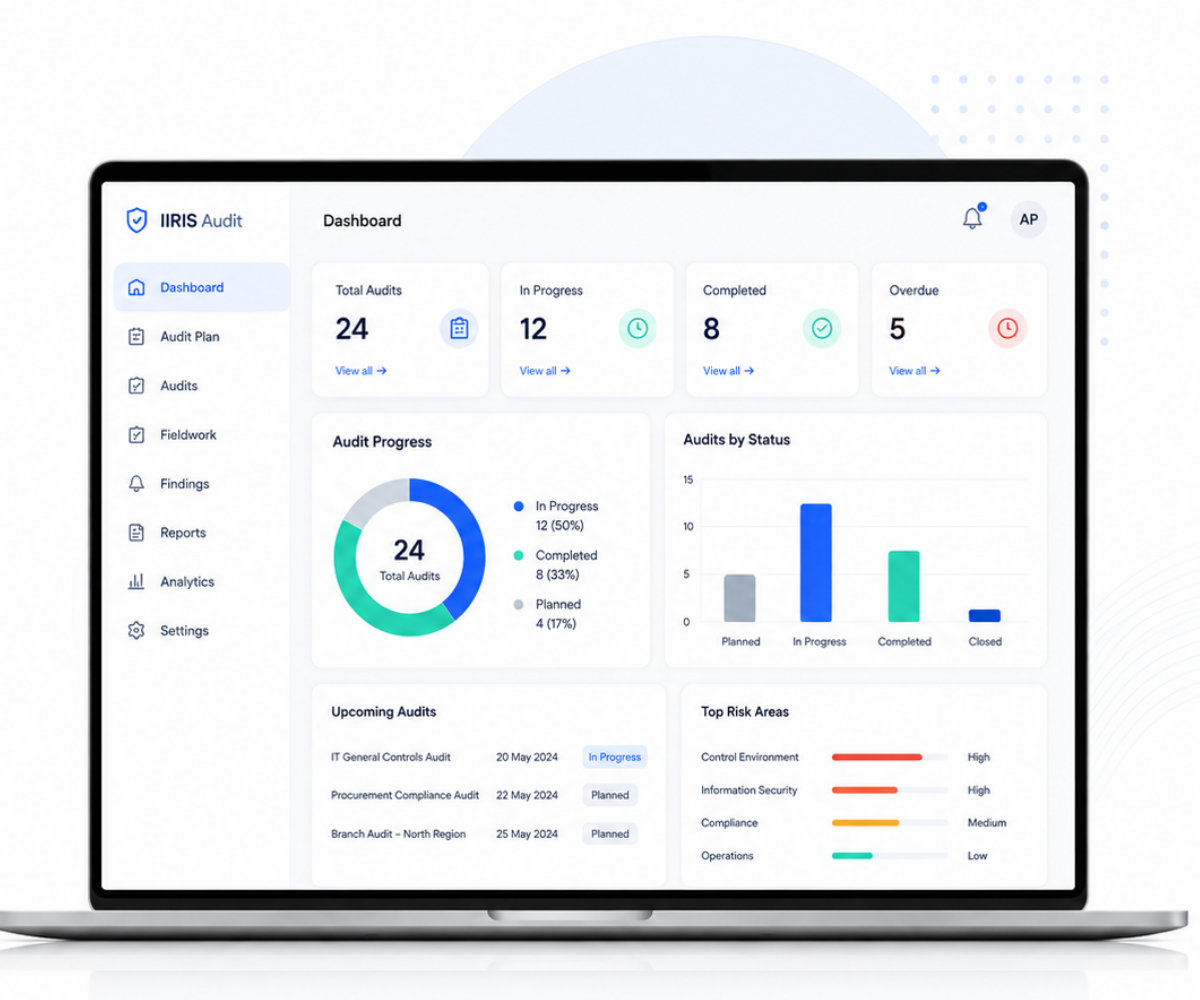
Audit operations from scheduling and fieldwork through to the issued report, on one platform.
The platform generates the audit instrument, carries the auditor through fieldwork online or offline, and issues the finished report from the same record. Preparation and compilation, which ordinarily consume more time than the audit itself, are absorbed by the system.
Internal audit functions, risk management teams and audit service providers running recurring programmes across many locations, including sites where connectivity is limited.
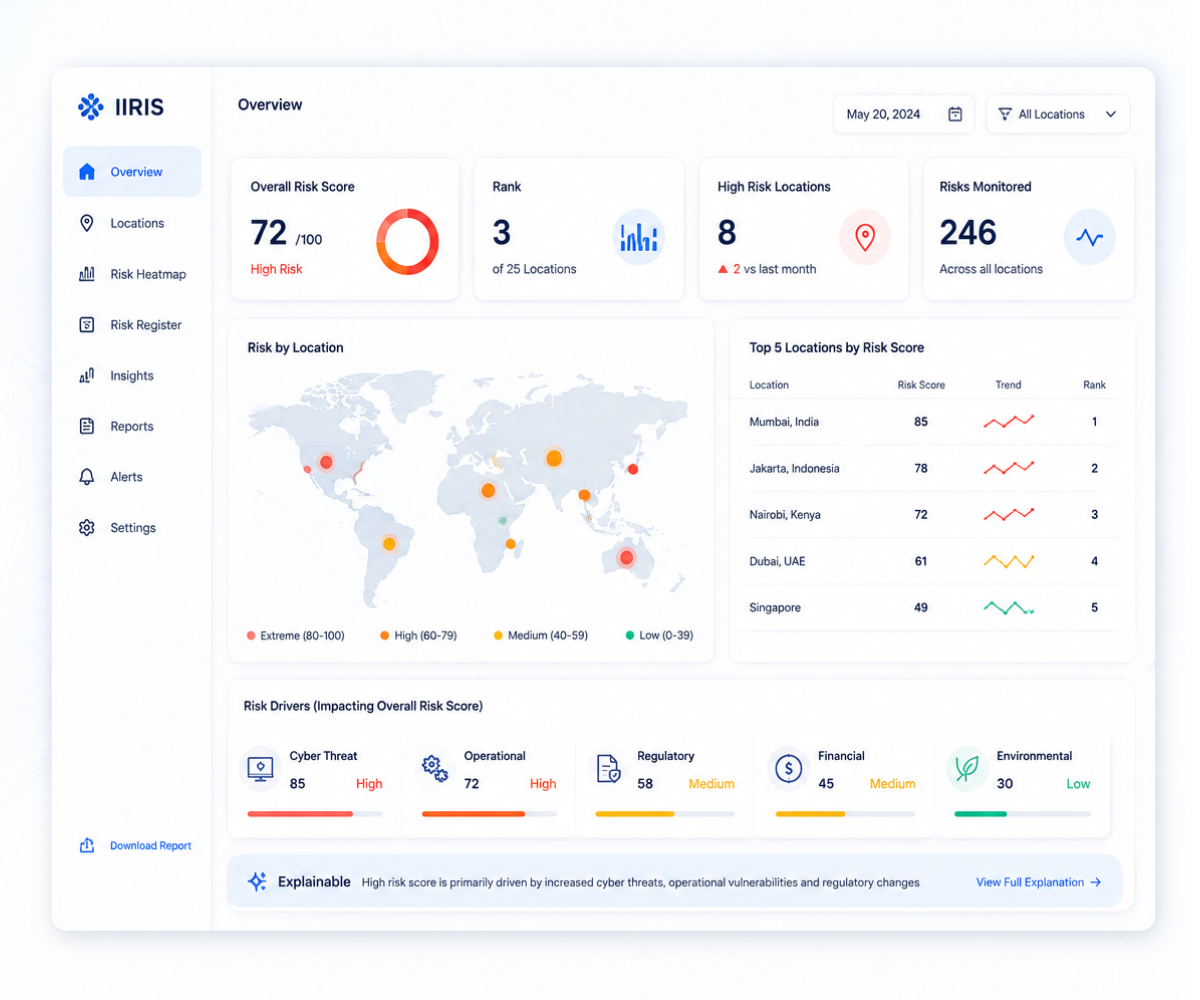
A single risk position across every location, scored, ranked and explainable to the level of its drivers.
Alarms, incidents, audit findings and external intelligence are consolidated into one location wise position. Every score decomposes into the factors that produced it, which is what allows it to be acted on and contested.
Corporate security and facility leadership accountable for distributed estates, and group structures requiring entity level separation beneath a consolidated view.
Consent and data principal rights managed as a controlled lifecycle, with the evidence retained throughout.
The platform establishes, for any individual on any date, what was asked, which notice version applied, what was granted, what was subsequently withdrawn and where that instruction propagated. That reconstruction is the substance of Digital Personal Data Protection Act compliance.
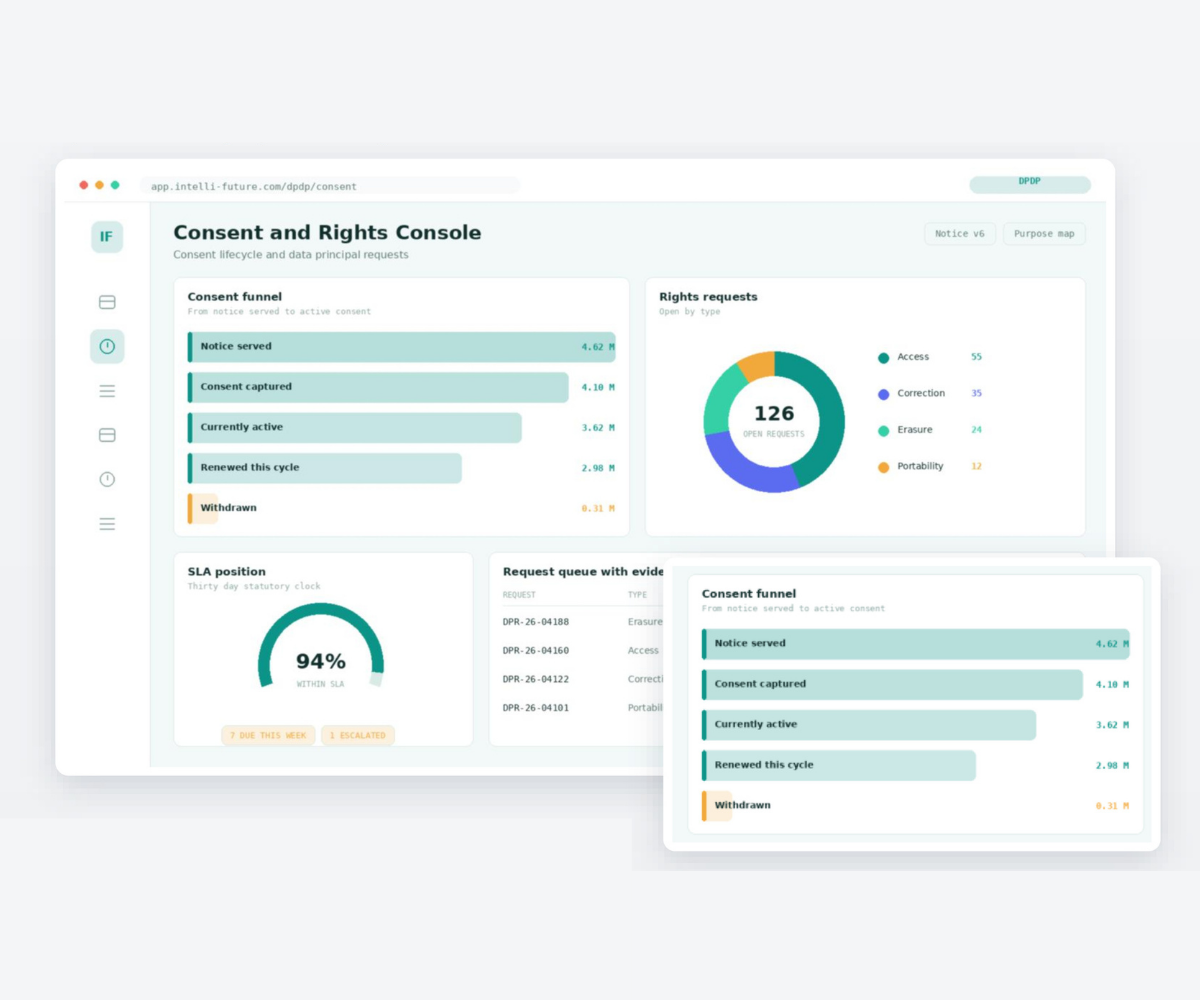
Organisations processing personal data at scale under the Digital Personal Data Protection Act, particularly where consent has accumulated across several channels over several years.
Investigative capability at institutional scale, evidenced to a standard that withstands challenge. This is the discipline closest to the group's own practice.
Command over every criminal case and fraud matter the organisation carries, from registration through closure and recovery.
A portfolio of several thousand matters is held as a live, verified position rather than a register of reference numbers. Status is established by attendance and dated, so what the platform reports is what is on the file.
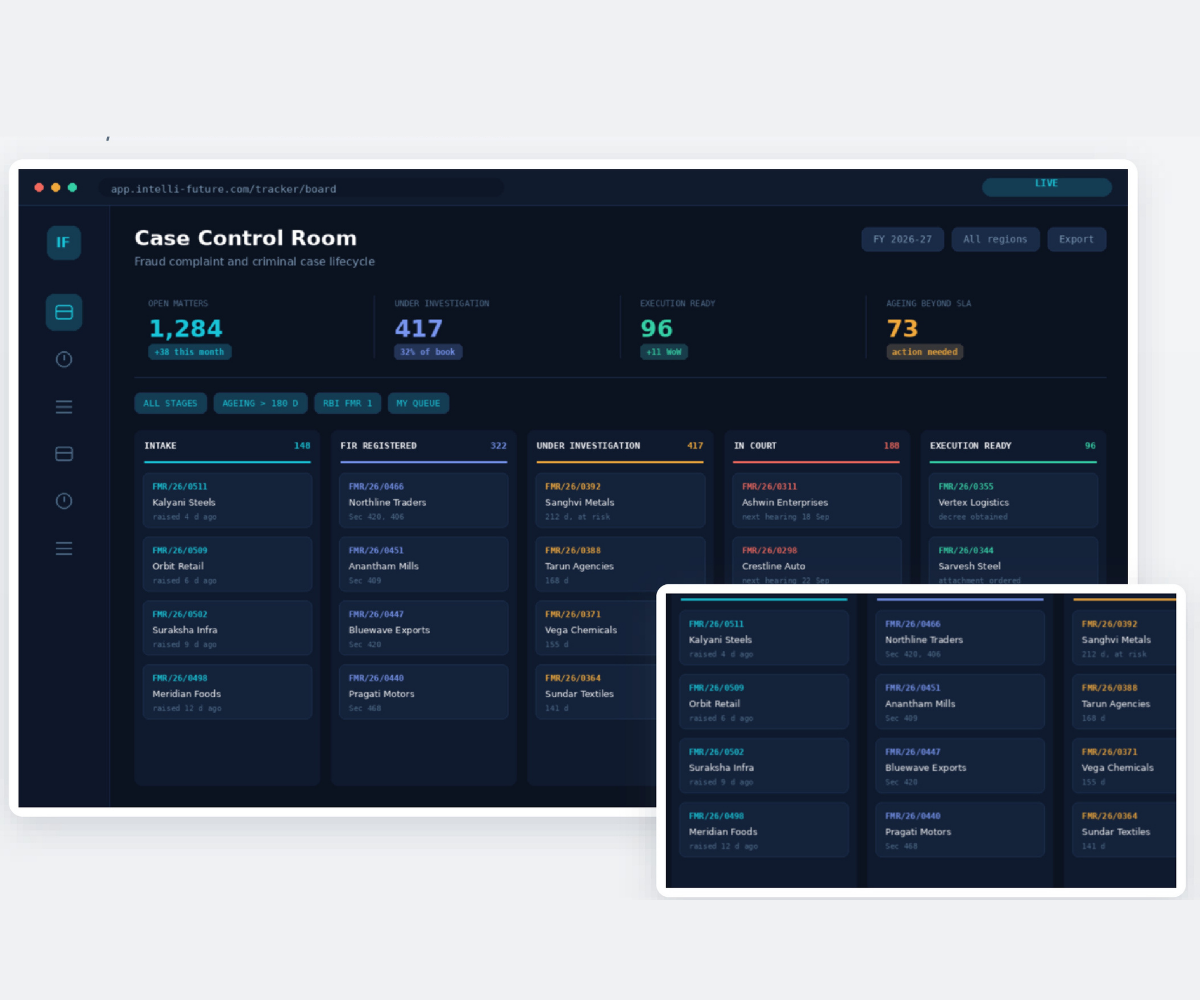
The position as handed over, treated as the starting point rather than the conclusion.
The position confirmed by a person who has attended and read the file, with the date of verification recorded.
Listing position, next date of action and documents due, taken from the record itself.
The order exists and enforcement remains. These are isolated so that recoverable matters are never carried among long horizon cases.
A document, statement or certification is outstanding. The specific gap is named against the matter.
A hearing, filing or appearance is due, with the alert scheduled against the date.
Progress turns on a correction, transfer, clerical error or jurisdiction question.
Movement has ceased. These are surfaced deliberately so closure becomes a decision.
Total matters under monitoring, their distribution, and verified against pending verification.
Cases filed by the organisation and cases filed against it, held separately throughout, with pending and confirmed closed counts under each.
The pending population resolved into the five stages, so queue size is visible before any matter is opened.
Search on the unique IIRIS reference. Returns police station, date of last verification, status per the police file, next steps, next date of action, IIRIS handler and client handler.
Quantum at risk is shown at portfolio level and sliced by branch or regional office, by direction and by stage, so accountability attaches to a number that is genuinely regional.
Notification reaches the nominated user one day before a date of action, while intervention remains possible.
A user sees only mapped matters. A lookup outside that mapping returns a not authorised response.
For banks, Fraud Monitoring Return formats generate from the same case data. For other organisations the module is disabled and does not appear.
Every matter is verified, categorised and loaded, after which monitoring is continuous. Capacity extends to 3,000 matters a month, on a six month minimum.
Engaged matter by matter. Execution ready cases are progressed with field support and law enforcement liaison, which is where recovery is realised.
Banks and non banking financial companies, logistics and delivery operations carrying cash collection exposure, retail and e commerce holding high volumes of low value matters, and manufacturing and infrastructure managing theft, diversion and contractor related complaints.
Asset and land record intelligence across Indian jurisdictions, gathered and evidenced at scale.
A single request clears the State and Union Territory land record portals in parallel. Extraction, transliteration and entity matching are handled by the platform, and every record carries its source and confidence.
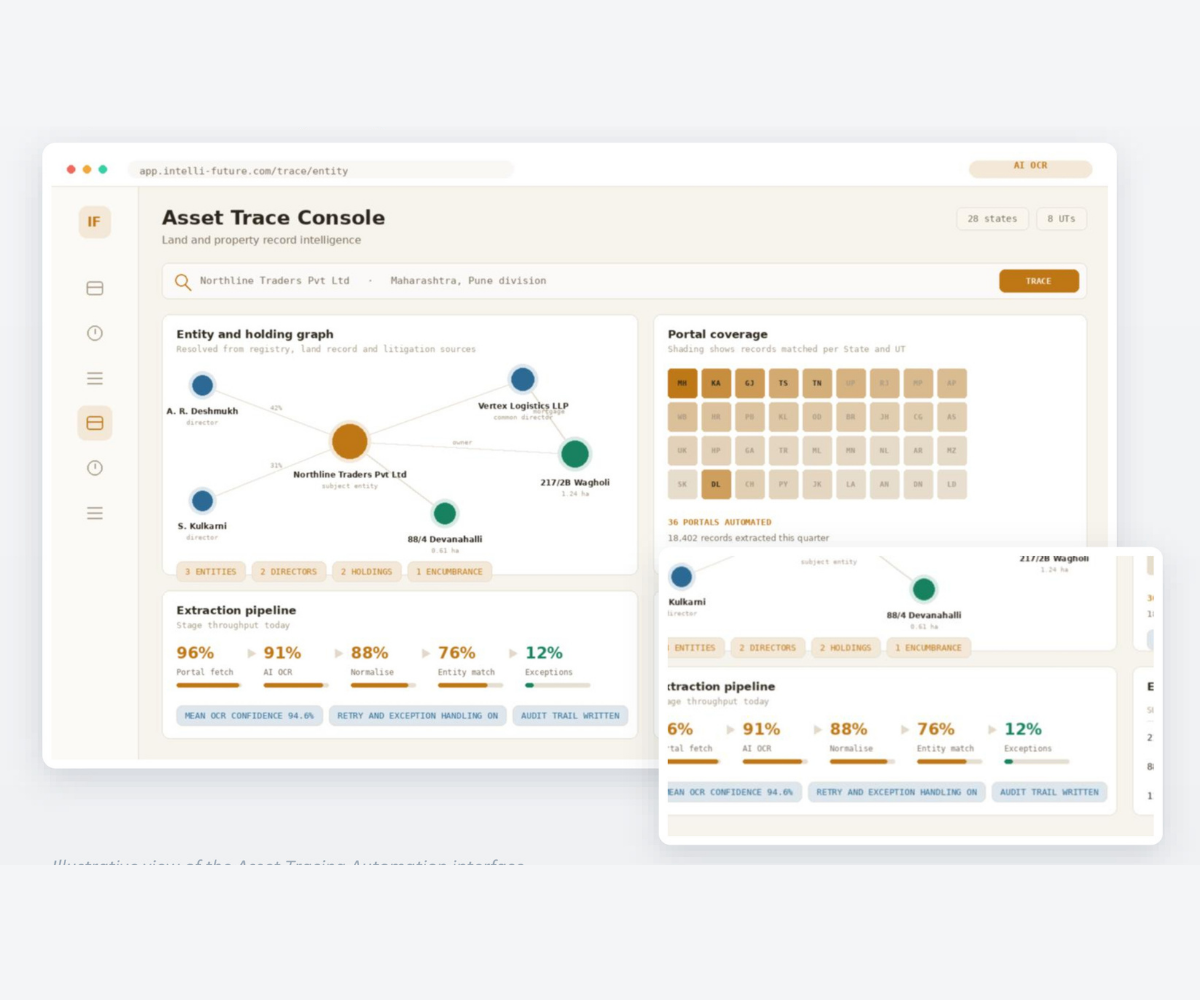
Investigation and recovery teams, lenders assessing security, law firms conducting asset discovery, and diligence practices where a conclusion must be evidenced rather than asserted.
Fraud assessment governed by the institution's own procedure, applied consistently at every desk.
Classification, supporting reference and the regulatory return are produced within a single conversation, anchored to the institution's approved procedure. Consistency between investigators becomes a property of the system rather than of individual recall.
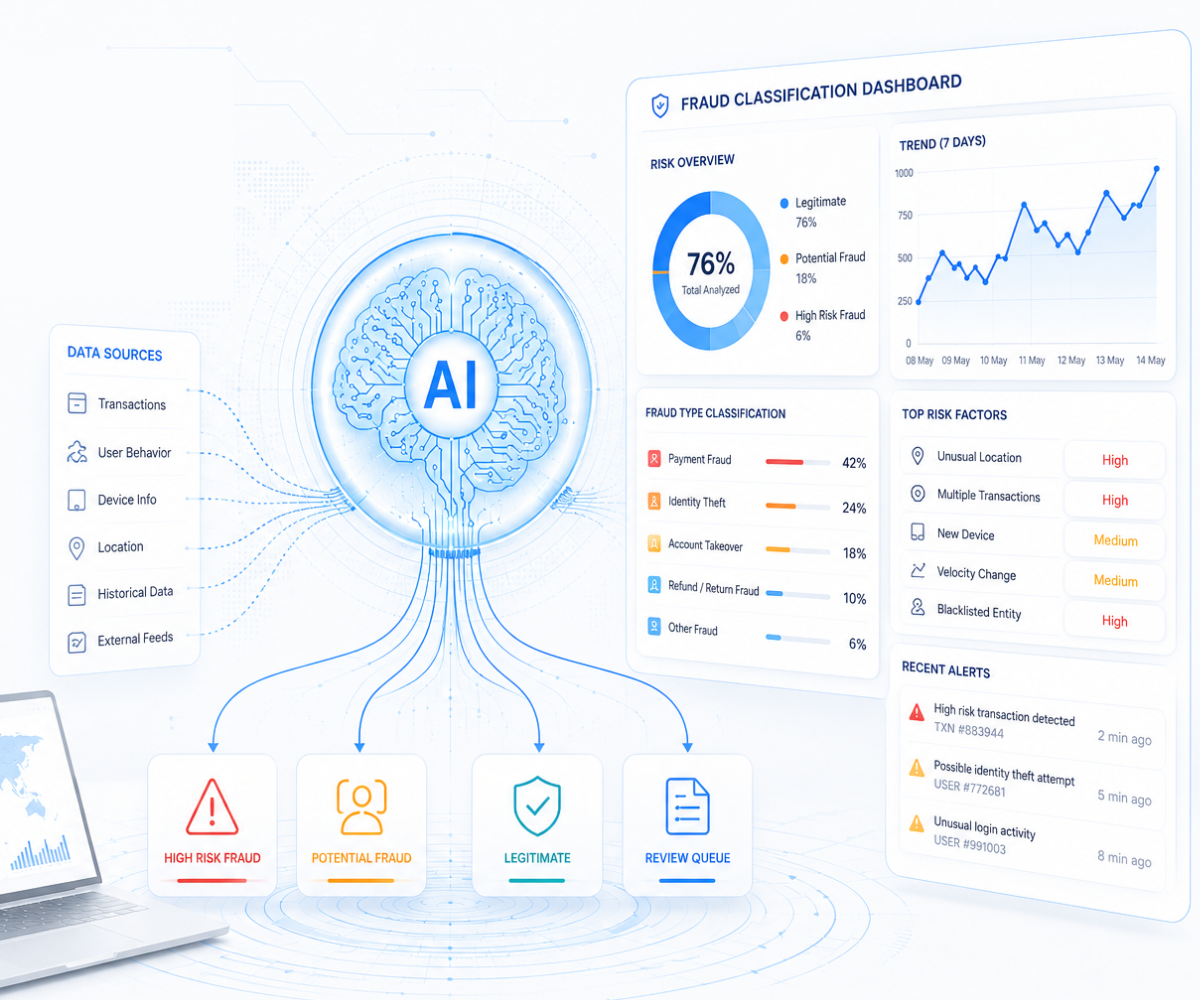
Bank fraud investigation functions, and institutions deploying a white label assistant across multiple entities or workflows.
The record an institution keeps of itself.
Institutional memory captured at the moment it is created and held as a permanent, searchable record.
What a distinguished visitor says is captured in their own voice and hand, converted into a structured record, and made retrievable by name, date, occasion or organisation for as long as the institution stands.
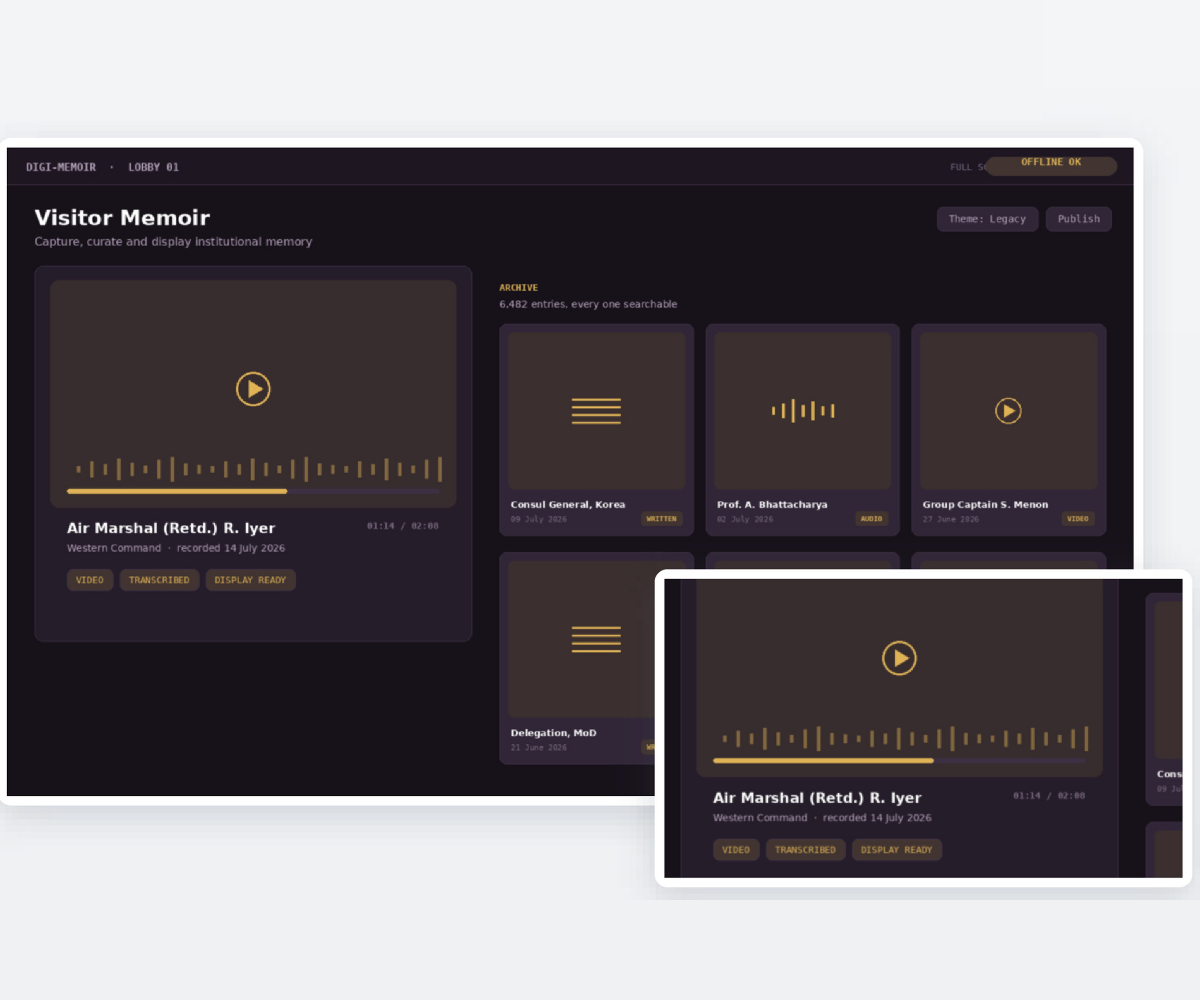
Defence establishments: Public relations centres, military headquarters, officer messes and dignitary guest houses.
Corporate environments: Head office lobbies, training institutions, innovation centres and executive lounges.
Clubs and hospitality: Elite clubs, VIP dining halls and round table auditoriums.
Memorials and museums: War memorials and museums holding veteran and visitor testimony.
Describe the mandate and we will identify which platform applies. Demonstrations run on your scenario rather than a prepared one.
Talk to our team